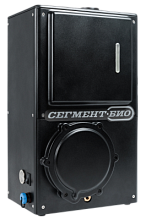
CPI Crypto – a means of protecting the perimeter, organizing virtual private networks (VPNs) and automatically encrypting / decrypting information that does not contain state secret information transmitted within such networks between geographically distributed objects via switched communication paths, including public networks, with the functions of managing the settings of such networks and their automatic distribution between them. nodes.
PAK IVK Krypto Isp. 2 AP-1 is a high-performance crypto gateway in the 1U form factor for building central nodes of crypto networks, equipping large-scale automation objects with high performance requirements.
The model range of CPI Krypto includes a Cryptonet Node Configuration Management Center (MCC) in two delivery options, several variants of hardware and software Gateways, an Automated workplace of the cryptonet administrator (Administrator's WORKSTATION), as well as a software Subscriber point.
Each CPI Crypto model, depending on its purpose, includes the necessary set of certified software and / or hardware tools.
Technical features: ensuring confidentiality and integrity control of data transmitted over channels by encryption and imitation protection in accordance with GOST, the ability to create a complex-subordinate cryptographic VPN network, the ability to choose the tcp or udp transport protocol for building a cryptographic VPN network or any part of it, the validity period of key information is 3 years.
Areas of application: in personal data information systems (ISPDn) up to the 1st level of security inclusive, in state information systems (GIS) up to the 1st class of security inclusive, ensuring the security of significant critical information infrastructure objects (CII) up to the 1st category inclusive.
The main functions of the cryptogluze IVK Krypto Isp. 2 AP-1: work in the router mode with confidentiality and integrity control of data transmitted over channels directly with the PAC by their encryption and imitoprotection method in accordance with GOST (cryptographic protection of transmitted data), work in the router mode without encryption/decryption of information flows, transparent work within the framework of the created data streams. virtual networks protected by cryptographic methods, protection of settings of virtual network nodes from unauthorized modification, guaranteed distribution of settings of nodes created by virtual networks, control of the integrity of the SCSI software, local configuration management, optimization (compression) of transmitted data in communication channels with low bandwidth, the ability to choose the tcp or udp transport protocol for building a cryptographic network or its separate section, the ability to end-to-end encryption and decryption of the information stream with mandatory tags in accordance with GOST R 58256-2018, the ability to install in a cluster (Stand-by).
Sealed container for installing an electronic identifier (key information carrier), APMDZ FSB certificate, DOE FSTEC certificate (type A, Class 4), SCSI FSB certificate (CS3)
Working hours: 8:00 - 18:00
Toll-free call in Russia